Lee DSilver badge
Reply Icon
The primary reason to remove code is maintenance burden.
Every time you want to change some underlying API, or migrate to a new primitive, or introduce new locking, you have a bunch of old code that receives really quite devasting changes that can't be automated... and there's nobody using or maintaining that code to check it still works properly in all possible instances. Then some pillock boots it up on their NAS products as part of their natural firmware upgrades, and it starts trashing customer's NAS data because of some niche side-effect, and now you have a major NAS vendor telling its customers that Linux isn't reliable and just trashed all their customer's filesystems.
As soon as something falls out of active maintenance, it has to be marked for deprecation to let people know not to use it, and if nobody steps up to maintain it, it gets removed.
Lack of maintenance is literally the primary reason for code removal in the Linux kernel. Things that should have been removed decades ago were still actively maintained, so they were allowed to stick around until the last maintainers left (not the last users!). Similarly, things that were brand-new but didn't have adequate maintenance were removed and pushed back out of tree. In fact, one of the main reasons for being refused to be pulled in-tree is that someone then has to maintain it forever. And that's a huge burden for code they may not understand, so it can take DECADES to get code into mainline simply because you have to break it down and get every piece in and slip it past all the maintainers before you ever get close to actually merging the final product, and then you have to prove that enough people will use it so that enough people will be around to maintain it so that kernel maintainers aren't spending half their life trying to fix issues in other people's code that they don't understand.
And this severely affects security. One locking or permission change, and if you don't go updating all your code you are leaving security holes in the kernel. That can't be allowed. And if there's nobody around to say "Yeah, I've fixed bcachefs against this new novel attack that we're seeing throughout the kernel code" then it gets removed. Quite rightly.
People think it's personalities, or technicalities, or some desire to just move into every new thing and throw away every old thing (which is utter nonsense, Linux supports some ridiculously antique stuff still), it's not. It's about maintenance. The one thing Linux lacks is good maintainers with time on their hands to do that job, usually for free! Those are the most valuable and precious resources. And, as things like NTFS filesystem support cough Paragon cough, whole-kernel mass-patches that nobody is willing to break down (cough grsecurity cough) etc. have found out... it doesn't matter how great your code is, if people aren't willing to maintain it you have a decades-long uphill battle to get it into the kernel, let alone keep it there.
Nobody wants to babysit your code in perpetuity, especially if... when a new maintainer is required... not one competent, trusted person is willing to step up and say "I'll do that".


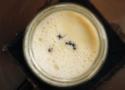
Ants carry lactic and acetic acid bacteria that help coagulate milk, as well as formic acid to acidify it
Fermenting milk to make yogurt, cheeses, or kefir is an ancient practice, and different cultures have their own traditional methods, often preserved in oral histories. The forests of Bulgaria and Turkey have an abundance of red wood ants, for instance, so a time-honored Bulgarian yogurt-making practice involves dropping a few live ants (or crushed-up ant eggs) into the milk to jump-start fermentation. Scientists have now figured out why the ants are so effective in making edible yogurt, according to a paper published in the journal iScience. The authors even collaborated with chefs to create modern recipes using ant yogurt.
Making social conversation doesn’t come naturally to everyone. Few individuals are adept at it because they are so focused on their own insecurities that it distracts them from reaching out.
The keys to social dexterity are: Be friendly. A smile is an excellent icebreaker because it puts others around you at ease. Be kind. Be honest. (Be a good listener and people will think you are a genius.) Show an interest in the people you meet by asking about their interests, but avoid “sensitive” topics, particularly in a business situation.
My “How to Be Popular” booklet contains many other tips on how to approach others, and what to say and not say when trying to make conversation. It can be ordered by sending your name and address, plus a check or money order for $8 (U.S. funds), to: Dear Abby Popularity Booklet, P.O. Box 446, Kings Mills, OH 45034-0446.
Earlier this year, Herschend agreed to buy Palace Entertainment and its 20 U.S. parks across 10 states from European theme park company Parques Reunidos. While Herschend may not be a household name, many theme park enthusiasts know some of its biggest assets, including Dollywood, Silver Dollar City, the Harlem Globetrotters, and Kentucky Kingdom.
The acquisition gave Herschend some of the country’s best-known theme parks, including Kennywood and Dutch Wonderland in Pennsylvania and Lake Compounce in Connecticut, America’s first theme park. Herschend Parks averages around 20 million visitors annually, putting it on par with United Parks and Resorts, owners of Busch Gardens and SeaWorld, who average around 21 million visitors annually.
However, Dollywood is the crown jewel of Herschend’s theme parks. The Dolly Parton creation is routinely voted the best theme park in America, beating out giants like Disney World and the Universal Orlando Resort.
Whether you know it or not, you’re in a battle. The battle does not end. It doesn’t stop because you’re busy. I’ve heard it said, “If the devil can’t make you bad he’ll make you busy.”
Maybe you don’t have an hour to have a full-on Bible study with your son. But you can use these four ideas to intentionally disciple him — whether you have ten minutes or two hours. These four ideas are the framework you can use to maximize time with your boys. //
- Listen: Build the Relationship
The point here is this: connect with your son.
- Read: Get into God’s Word
Take a moment to read the Bible yourself. Don’t get hung up on which part of the Bible. Make notes about what is significant to you. Then, share your heart with your son. It’s okay not to have all of the answers. You are revealing another world to your child. It does not have to be long or elaborate. In fact, shorter is probably better.
- Act: Apply the Word
This is the “so what” part. Maybe the verse you’re on is about behavior change. Maybe it’s about service or how to treat your neighbor. Do your best to apply truth in love.
Whenever possible live out what you read with your son.
4 Pray: Talk with God
Close time with your son with prayer, simply talking with God about what you’re learning and praying for, and with your son. Additionally, keeping a journal of prayer requests and seeing together the Lord answer can be a powerful means to see God work overtime.
The creative constituents of Western music have a choice to make: continue manifesting hell on earth, or begin magnifying redemption through their art.
Music is a balance of tension and resolution. A mentor once told me that the greatest composers are those who demonstrate mastery of this basic tenet. Dissonance, one form of musical tension, empowers harmony and resolution when used well. However, with few exceptions, today’s composers reject the natural order of tension and resolution. They opt instead to create sonic nightmares, soundscapes smeared upon a postmodern canvas in which tonality is subjective. There is never a true resolution, only growing ugliness.
That is why the celebration of the work of Estonian composer Arvo Pärt, who turned 90 on Sept. 11, offers more than a glimmer of hope. Pärt, whose style of composing is indelibly intertwined with his Orthodox Christian faith, is being celebrated at Carnegie Hall and around the world for creating music that is beautiful in a time when ugliness is preferred. //
Pärt’s musical legacy is one that very few composers, of this century or others, will hold a candle to. Still, a handful of other current composers are breathing life into the landscape. In the choral world, it is no wonder that composer Eric Whitacre has attained cult-status. His music, while reputably redundant, is beautiful; choirs enjoy singing his work, and audiences love hearing it. His piece “Lux Aurumque” has been streamed more than 9 million times on Spotify alone. Yet Whitacre is largely dismissed by the same art composers and academic superiors whose own music suffers from terminal unlikability. //
Great suffering can produce a person who resembles the devil, but it can also produce a person who resembles God. The difference is how one suffers; suffering can be sanctifying.
Contemporary art music embodies suffering without sanctification, and thus, it has fallen from beauty to ugliness. Art embodies ugliness only when suffering is glorified for its own sake, rather than as a means to an end: sanctification and ultimately, redemption.
In a social media post last week, President Trump noted that what Democrats are demanding in exchange for their cooperation in reopening government would require more than $1 trillion in spending and “force Taxpayers to fund Transgender surgery for minors.” Indeed, taxpayers are already funding such surgeries via Obamacare subsidies — and Democrats have shut the government down as they demand that Covid-era enhanced Obamacare subsidies, which expire on Dec. 31, keep flowing to insurers covering these treatments. //
Take Colorado, which requires all insurers to cover so-called “gender affirming care” as an essential health benefit. The state’s Division of Insurance lists all the surgical and hormonal treatments that insurers cover. The list, which runs the gamut from facial feminization to gluteal implantation and implantation of testicular prostheses, includes treatments that many Americans would at best find wasteful and at worst consider morally objectionable and offensive: //
Unfortunately, Colorado is not an outlier. The Movement Advancement Project notes that 24 states have “nondiscrimination” provisions in their insurance markets. In these states, insurers that cover procedures like mastectomies for breast cancer must also cover the same procedure as part of so-called “gender affirming care.”
Recently declassified documents indicate leaks of classified information to reporters were designed to portray Trump as in league with Russia.
Recently declassified documents indicate that people close to former FBI Director James Comey and Democratic Sen. Adam Schiff were connected to leaks of classified information to prominent reporters designed to portray Donald Trump and his allies as being in league with Russia.
Open Source Blueprints for Civilization. Build Yourself.
We’re developing open source industrial machines that can be made for a fraction of commercial costs, and sharing our designs online for free. The goal of Open Source Ecology is to create an open source economy – an efficient economy which increases innovation by open collaboration.
Notepad++ is a free (as in “free speech” and also as in “free beer”) source code editor and Notepad replacement that supports several programming languages. Running in the MS Windows environment, its use is governed by GNU General Public License.
Based on the powerful editing component Scintilla, Notepad++ is written in C++ and uses pure Win32 API and STL which ensures a higher execution speed and smaller program size.
The result is Notepad2, a fast and light-weight Notepad-like text editor with syntax highlighting. This program can be run out of the box without installation, and does not touch your system's registry.
Aranya is an access governance and secure data exchange platform for organizations to control their critical data and services. Access governance is a mechanism to define, enforce, and maintain the set of rules and procedures to secure your system’s behaviors. Aranya gives you the ability to apply access controls over stored and shared resources all in one place.
Aranya enables you to safeguard sensitive information, maintain compliance, mitigate the risk of unauthorized data exposure, and grant appropriate access. Aranya’s decentralized platform allows you to define and enforce these sets of policies to secure and access your resources.
The platform provides a software toolkit for policy-driven access controls and secure data exchange. The software is deployed on endpoints, integrating into applications which require granular access controls over their data and services. Endpoints can entrust Aranya with their data protection and access controls so that other applications running on the endpoint need only to focus on using the data for their intended functionality. Aranya has configurable end-to-end encryption built into its core as a fundamental design principle.
A key discriminating attribute of Aranya is the decentralized, zero trust architecture. Through the integration of the software, access governance is implemented without the need for a connection back to centralized IT infrastructure. With Aranya’s decentralized architecture, if two endpoints are connected to each other, but not back to the cloud or centralized infrastructure, governance over data and applications will be synchronized between peers and further operations will continue uninterrupted.

In tcsh, you can do:
(ls $argv > filelist) >& /dev/nullNote that >& redirects both stdout and stderr, but since stdout has already been redirected elsewhere only the stderr will make it through to /dev/null
Today’s world requires us to make complex and nuanced decisions about our digital security. Evaluating when to use a secure messaging app like Signal or WhatsApp, which passwords to store on your smartphone, or what to share on social media requires us to assess risks and make judgments accordingly. Arriving at any conclusion is an exercise in threat modeling.
Are your links not malicious looking enough?
This tool is guaranteed to help with that!
What is this and what does it do?
This is a tool that takes any link and makes it look malicious. It works on the idea of a redirect. Much like https://tinyurl.com/ for example. Where tinyurl makes an url shorter, this site makes it look malicious.
Place any link in the below input, press the button and get back a fishy(phishy, heh...get, it?) looking link. The fishy link doesn't actually do anything, it will just redirect you to the original link you provided.
Notion just released version 3.0, complete with AI agents. Because the system contains Simon Willson’s lethal trifecta, it’s vulnerable to data theft though prompt injection.
First, the trifecta:
The lethal trifecta of capabilities is:
- Access to your private data—one of the most common purposes of tools in the first place!
- Exposure to untrusted content—any mechanism by which text (or images) controlled by a malicious attacker could become available to your LLM
- The ability to externally communicate in a way that could be used to steal your data (I often call this “exfiltration” but I’m not confident that term is widely understood.)
This is, of course, basically the point of AI agents. //
The fundamental problem is that the LLM can’t differentiate between authorized commands and untrusted data. So when it encounters that malicious pdf, it just executes the embedded commands. And since it has (1) access to private data, and (2) the ability to communicate externally, it can fulfill the attacker’s requests. I’ll repeat myself:
This kind of thing should make everybody stop and really think before deploying any AI agents. We simply don’t know to defend against these attacks. We have zero agentic AI systems that are secure against these attacks. Any AI that is working in an adversarial environment—and by this I mean that it may encounter untrusted training data or input—is vulnerable to prompt injection. It’s an existential problem that, near as I can tell, most people developing these technologies are just pretending isn’t there.
It’s official: AOL’s dial-up internet has taken its last bow.
AOL previously confirmed it would be pulling the plug on Tuesday (Sept. 30) — writing in a brief update on its support site last month that it “routinely evaluates” its offerings and had decided to discontinue dial-up, as well as associated software “optimized for older operating systems,” from its plans.
Dial-up is now no longer advertised on AOL’s website. As of Wednesday, former company help pages like “connect to the internet with AOL Dialer” appeared unavailable — and nostalgic social media users took to the internet to say their final goodbyes.
Shootings at houses of worship and religious schools are happening at an alarming rate. I’m not just talking about Christian churches either; assailants have hit synagogues and Mormon congregations as well. As I write this, news of a stabbing attack at a synagogue in the UK on Yom Kippur is fresh on my mind as well.
What are churches to do? I’ve never been one to call for gun control and never will be — besides, the UK’s gun-grabbing fanaticism has only made stabbings more of a threat, as the Yom Kippur attack demonstrates. //
“Reverend, if you’re going to reprimand me, at least let me indulge my habit of quoting scripture and dead philosphers, after all somebody has to keep Augustine from rolling in his grave. Our Lord said ‘But now, if you have a purse, take it, and also a bag; and if you don't have a sword, sell your cloak and buy one.’
Also, Thomas Aquinas wrote in his Summa Theologica: 'one who defends his life is not guilty of murder, even if he is forced to deal a fatal blow, for it is preferable to defend oneself than to submit to the will of evildoers."
And as Edmund Burke—famously reminded us: ‘The only thing necessary for the triumph of evil is for good men to do nothing.’
But, Reverend, I want to be clear: I’m not standing guard. I’m just sitting in the pews like everyone else—albeit with a little extra peace of mind in under my jacket in case trouble finds us.” And I patted my hip holster.
I want to change The GUI Listen Address from 127.0.0.1:8384 to 0.0.0.0:8384 from syncthong cli config gui
syncthing cli config gui raw-address set 0.0.0.0:8384